
What applies when, after the Digital Omnibus
First question: are you a provider or a deployer?
Five questions to classify your system
Worked examples
Article 50 in practice
If your system is high-risk
The GDPR still applies alongside
Who supervises in Germany
Checklist
How we can help
FAQ
Is an AI agent high-risk under the EU AI Act?
When do the AI Act's high-risk rules apply after the Digital Omnibus?
Do we need to tell users they are talking to an AI?
We build on GPT or Claude. Who is the provider?
Does a RAG chatbot need to mark its answers as AI-generated?
Who enforces the AI Act in Germany?
What are the fines?
Sources
The EU AI Act for AI Agents and RAG Systems in 2026: A Classification Checklist

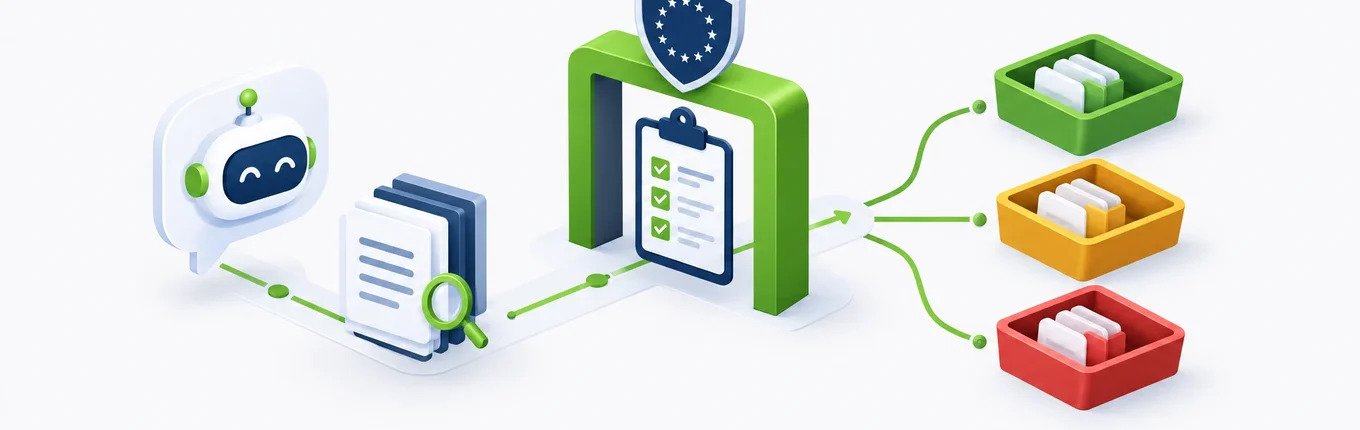
Short answer (October 2026). Most AI agents and RAG assistants that companies build are not high-risk under the EU AI Act, but almost all of them have obligations already. Since 2 August 2026, Article 50 requires that people are told they are interacting with an AI system at the latest at the first interaction, and providers of generative systems must mark synthetic content in a machine-readable way; systems already on the market have until 2 December 2026 for the marking. If you build an agent on GPT, Claude or Mistral and offer it under your own name, you are the provider of that AI system. It becomes high-risk only if it is used for an Annex III purpose such as recruiting, decisions about workers, credit scoring or life and health insurance pricing; the Digital Omnibus moved those obligations to 2 December 2027. Breaches of the transparency duty can cost up to €15 million or 3% of worldwide turnover, and in Germany the Bundesnetzagentur supervises compliance under the KI-MIG since July 2026.
This checklist is for companies that build or buy AI agents and RAG systems. It updates our August overview of the AI Act and AI agents with the final Digital Omnibus text and adds a classification test with worked examples.
What applies when, after the Digital Omnibus

The Digital Omnibus on AI, Regulation (EU) 2026/1744, was published on 24 July 2026 and entered into force on 27 July 2026. For builders of agents and RAG systems it changed four things:
- High-risk obligations moved. For Annex III uses they apply from 2 December 2027, for AI in products covered by Annex I (machinery, medical devices and similar) from 2 August 2028.
- A grace period for marking, and only for marking. Providers of generative systems placed on the market before 2 August 2026 have until 2 December 2026 to comply with Article 50(2). The rest of Article 50 applies since 2 August 2026.
- AI literacy was softened. Article 4 now requires providers and deployers to take measures to support the AI literacy of staff who operate AI systems on their behalf; it no longer requires guaranteeing a specific level for each person.
- Lighter rules for small companies. Simplified documentation and a proportionate quality management system now also cover small mid-cap companies, and their fines for most obligations are capped at the lower of the two amounts.
First question: are you a provider or a deployer?
The AI Act distinguishes the provider, who develops an AI system or has it developed and places it on the market or puts it into service under its own name (Article 3(3)), from the deployer, who uses an AI system under its authority in a professional context (Article 3(4)).
- You build an agent or RAG assistant on a model API and offer it to customers or use it under your name: you are the provider of the AI system. OpenAI, Anthropic, Google or Mistral are providers of the general-purpose AI model; their obligations under Articles 53 to 55 apply since August 2025 and do not transfer to you. Under the Commission's guidelines, a company that fine-tunes a model becomes a model provider itself only if the modification uses more than a third of the original training compute.
- You buy a ready-made assistant and use it internally: you are the deployer.
- The role can shift. Under Article 25, a deployer or distributor becomes the provider of a high-risk system if it puts its name on it, substantially modifies it, or changes the intended purpose of a system that was not high-risk so that it becomes high-risk. Connecting a general chatbot to your recruiting process is exactly such a change.
Five questions to classify your system

- Is it prohibited? Article 5 has applied since 2 February 2025. It bans, among other things, manipulative or deceptive techniques that cause significant harm, exploiting vulnerabilities due to age, disability or a specific social or economic situation, social scoring, and inferring emotions at the workplace or in education, except for medical or safety reasons. An agent that pushes vulnerable customers into contracts, or an assistant that reads employees' emotions from calls, is not a compliance project but a redesign.
- Is it used for an Annex III purpose? The relevant entries for agents are recruiting and selection (filtering applications, evaluating candidates), decisions about workers (promotion, termination, allocating tasks based on behaviour or personal traits, monitoring performance), creditworthiness and credit scores (fraud detection is excluded), risk assessment and pricing in life and health insurance, education and access to public benefits.
- Does an exception apply? Under Article 6(3), an Annex III system is not high-risk if it does not materially influence the outcome of decisions, because it only performs a narrow procedural task, improves the result of a completed human activity, detects deviations from prior decisions without replacing human review, or performs a preparatory task. Two conditions remain: a system that profiles natural persons is always high-risk, and a provider that relies on the exception must document its assessment and register the system.
- Does it interact with people or generate content? Then Article 50 applies (next section).
- Everything else has the baseline: AI literacy measures, the GDPR and sound contracts with the model provider.
The Commission published draft guidelines on high-risk classification in May 2026; the final version is still pending, so borderline cases deserve a written assessment now.
Worked examples
| System | Annex III? | Classification | What to do |
|---|---|---|---|
| Customer intake agent in chat, e-mail and messengers | no | limited risk | disclose AI at the first message; log conversations; a person approves the request |
| RAG assistant over internal manuals and policies for staff | no | minimal risk | AI literacy, access control, GDPR; disclosure if it is not obvious |
| RAG assistant for tax and accounting questions | no | minimal risk | as above; answers with sources and a "not found" path |
| Agent that handles shipment exceptions | no | minimal risk | disclosure when it writes to customers or drivers |
| Agent that pre-screens job applications | yes, 4(a) | high-risk from 2 December 2027 | provider obligations, human oversight, inform candidates |
| Agent that assigns tasks and rates staff performance | yes, 4(b) | high-risk; emotion recognition would be prohibited | inform the works council before use (Article 26(7)) |
| Agent that pre-checks creditworthiness | yes, 5(b) | high-risk, fundamental rights impact assessment for deployers | fraud detection alone is excluded |
| Marketing texts generated by AI | no | Article 50(2) for the provider; 50(4) only for public-interest texts | human editorial responsibility removes the 50(4) disclosure |
Two of these are our own projects: the AI Intake Agent is a customer-facing assistant under Article 50(1), and its configuration for a radiology service is deliberately limited to information and orientation. It does not interpret studies or give diagnoses; if it did, the question would no longer be the AI Act alone but medical device law, and with it Annex I.
Article 50 in practice
- Article 50(1), providers: a system that interacts directly with people must be designed so they know they are dealing with an AI, unless it is obvious to a reasonably well-informed, observant person. A line such as "I am an AI assistant of …" at the start of the conversation, also in e-mail and messenger channels, is the usual answer.
- Article 50(2), providers of generative systems: synthetic audio, images, video and text must be marked in a machine-readable format and detectable as artificially generated. Assistive editing that does not substantially change the input is exempt. The Commission confirmed the Code of Practice on transparency of AI-generated content, published in June 2026, as an adequate voluntary tool; about 190 organisations had signed by the end of July 2026.
- Article 50(4), deployers: deepfakes must be disclosed, and so must AI-generated text published to inform the public on matters of public interest, unless a person has reviewed it and someone holds editorial responsibility.
- Article 50(5), timing: the information must be clear and distinguishable at the latest at the first interaction or exposure.
The Commission published guidelines on the transparency obligations in July 2026. Breaching Article 50 falls in the fine tier of up to €15 million or 3% of worldwide annual turnover, whichever is higher; for SMEs the lower of the two applies.
If your system is high-risk
From 2 December 2027, the provider of an Annex III system needs a risk management system, data governance, technical documentation, automatic logging, instructions for use, human oversight, accuracy and robustness measures, a quality management system, a conformity assessment and registration in the EU database (Articles 9 to 17, 43 and 49). The deployer must use it according to the instructions, assign competent human oversight, check that input data is relevant, keep logs for at least six months, inform workers' representatives before using it at work and inform people affected by its decisions (Article 26). Public bodies and deployers of credit and insurance systems also need a fundamental rights impact assessment, which can now build on the GDPR data protection impact assessment (Article 27).
Fourteen months is not long for that list. A recruiting or credit agent that goes live in 2026 should be built with logging, oversight and documentation from the start.
The GDPR still applies alongside
A RAG system or agent that processes personal data needs a legal basis, a data processing agreement with the model provider and, for many uses, a data protection impact assessment. Under Article 22 GDPR, people have the right not to be subject to decisions based solely on automated processing that have legal or similarly significant effects, so an agent that decides alone about applications, credit or contracts needs either an exception or a person in the loop. The EDPB's Opinion 28/2024 adds that a model developed with unlawfully processed personal data can affect the lawfulness of its later use, which is a question to ask model vendors.
Who supervises in Germany
The KI-Marktüberwachungs- und Innovationsförderungsgesetz (KI-MIG) of 22 July 2026 entered into force on 29 July 2026 and names the Bundesnetzagentur as the market surveillance authority for the AI Act; BaFin supervises AI tied to regulated financial activity. The Bundesnetzagentur's AI service desk offers a free "Compliance Kompass" to check which obligations apply to a system.
Checklist
- List every AI system you build or use, with its purpose and users.
- Decide your role per system: provider, deployer or both.
- Rule out Article 5 practices, including emotion recognition at work.
- Check each purpose against Annex III; write down the reasoning, especially when you rely on Article 6(3).
- Add AI disclosure at the first interaction in every channel.
- Mark generated media and text where you are the provider; check the Code of Practice.
- Train the people who operate and supervise the systems (Article 4).
- Run a data protection impact assessment where personal data is processed; keep a person in the loop for significant decisions.
- Check contracts with model providers: data use, processing location, logs.
- For high-risk uses, start the documentation, logging and oversight design now for 2 December 2027.
How we can help
We build agentic AI applications and custom RAG systems with disclosure, logging, human approval and access control designed in, and we help classify existing systems before the deadlines. For the data protection side of model choice, see our article on local LLMs versus cloud APIs for sensitive data.
This article explains the regulation; it is not legal advice.
FAQ
Is an AI agent high-risk under the EU AI Act?
Usually not. An agent is high-risk only if it is used for a purpose listed in Annex III, such as recruiting, decisions about workers, credit scoring or life and health insurance pricing, and no Article 6(3) exception applies. Most customer service agents and RAG assistants are not high-risk but must meet the transparency duty of Article 50.
When do the AI Act's high-risk rules apply after the Digital Omnibus?
From 2 December 2027 for Annex III uses and from 2 August 2028 for AI in products covered by Annex I, under Regulation (EU) 2026/1744.
Do we need to tell users they are talking to an AI?
Yes. Since 2 August 2026, providers must design systems that interact with people so that they are informed at the latest at the first interaction, unless it is obvious.
We build on GPT or Claude. Who is the provider?
You are the provider of the AI system you offer under your name. OpenAI, Anthropic and other model makers are providers of the general-purpose model, with their own obligations since August 2025.
Does a RAG chatbot need to mark its answers as AI-generated?
The provider of a generative system must mark synthetic text in a machine-readable way under Article 50(2); systems already on the market before 2 August 2026 have until 2 December 2026. Separately, users must be told they are talking to an AI.
Who enforces the AI Act in Germany?
The Bundesnetzagentur, under the KI-MIG in force since 29 July 2026; BaFin for AI in regulated financial activities.
What are the fines?
Up to €35 million or 7% of worldwide turnover for prohibited practices, up to €15 million or 3% for other obligations including transparency, and up to €7.5 million or 1% for incorrect information. For SMEs, the lower amount applies.
Sources
- Regulation (EU) 2026/1744 (Digital Omnibus on AI), Official Journal, 24 July 2026
- Regulation (EU) 2024/1689 (AI Act), Articles 3, 4, 5, 6, 25, 26, 27, 50, 99, 113 and Annex III
- Hunton Andrews Kurth, EU Digital Omnibus on AI enters into force, July 2026
- European Commission, Code of Practice on transparency of AI-generated content and guidelines on transparency obligations, 2026
- European Commission, draft guidelines on the classification of high-risk AI systems, May 2026
- European Commission, General-purpose AI Code of Practice; WilmerHale, Commission guidelines for providers of general-purpose AI models, July 2025
- KI-Marktüberwachungs- und Innovationsförderungsgesetz (KI-MIG), BGBl. 2026 I Nr. 223
- Bundesnetzagentur, AI service desk, July 2025
- GDPR, Article 22; EDPB, Opinion 28/2024 on AI models
Categories
About the author
CTO & co-founder at Software Development Hub. Software engineer with 20+ years of experience. Python/Django-geek, software architect and IT team leader. Staying up-to-date with tech trends. Strong technical skills and diverse expertise in software structure design, development, team management and cybersecurity.
Share


Need a project estimate?
Drop us a line, and we provide you with a qualified consultation.